 Omnio
OmnioIQ · Company
Security, stated plainly.
How the platform and the data within it are protected. Only what is true today, and nothing more.
Access and transport
Signed in, and encrypted on the way.
Tracking links
Personal details wait for a check.
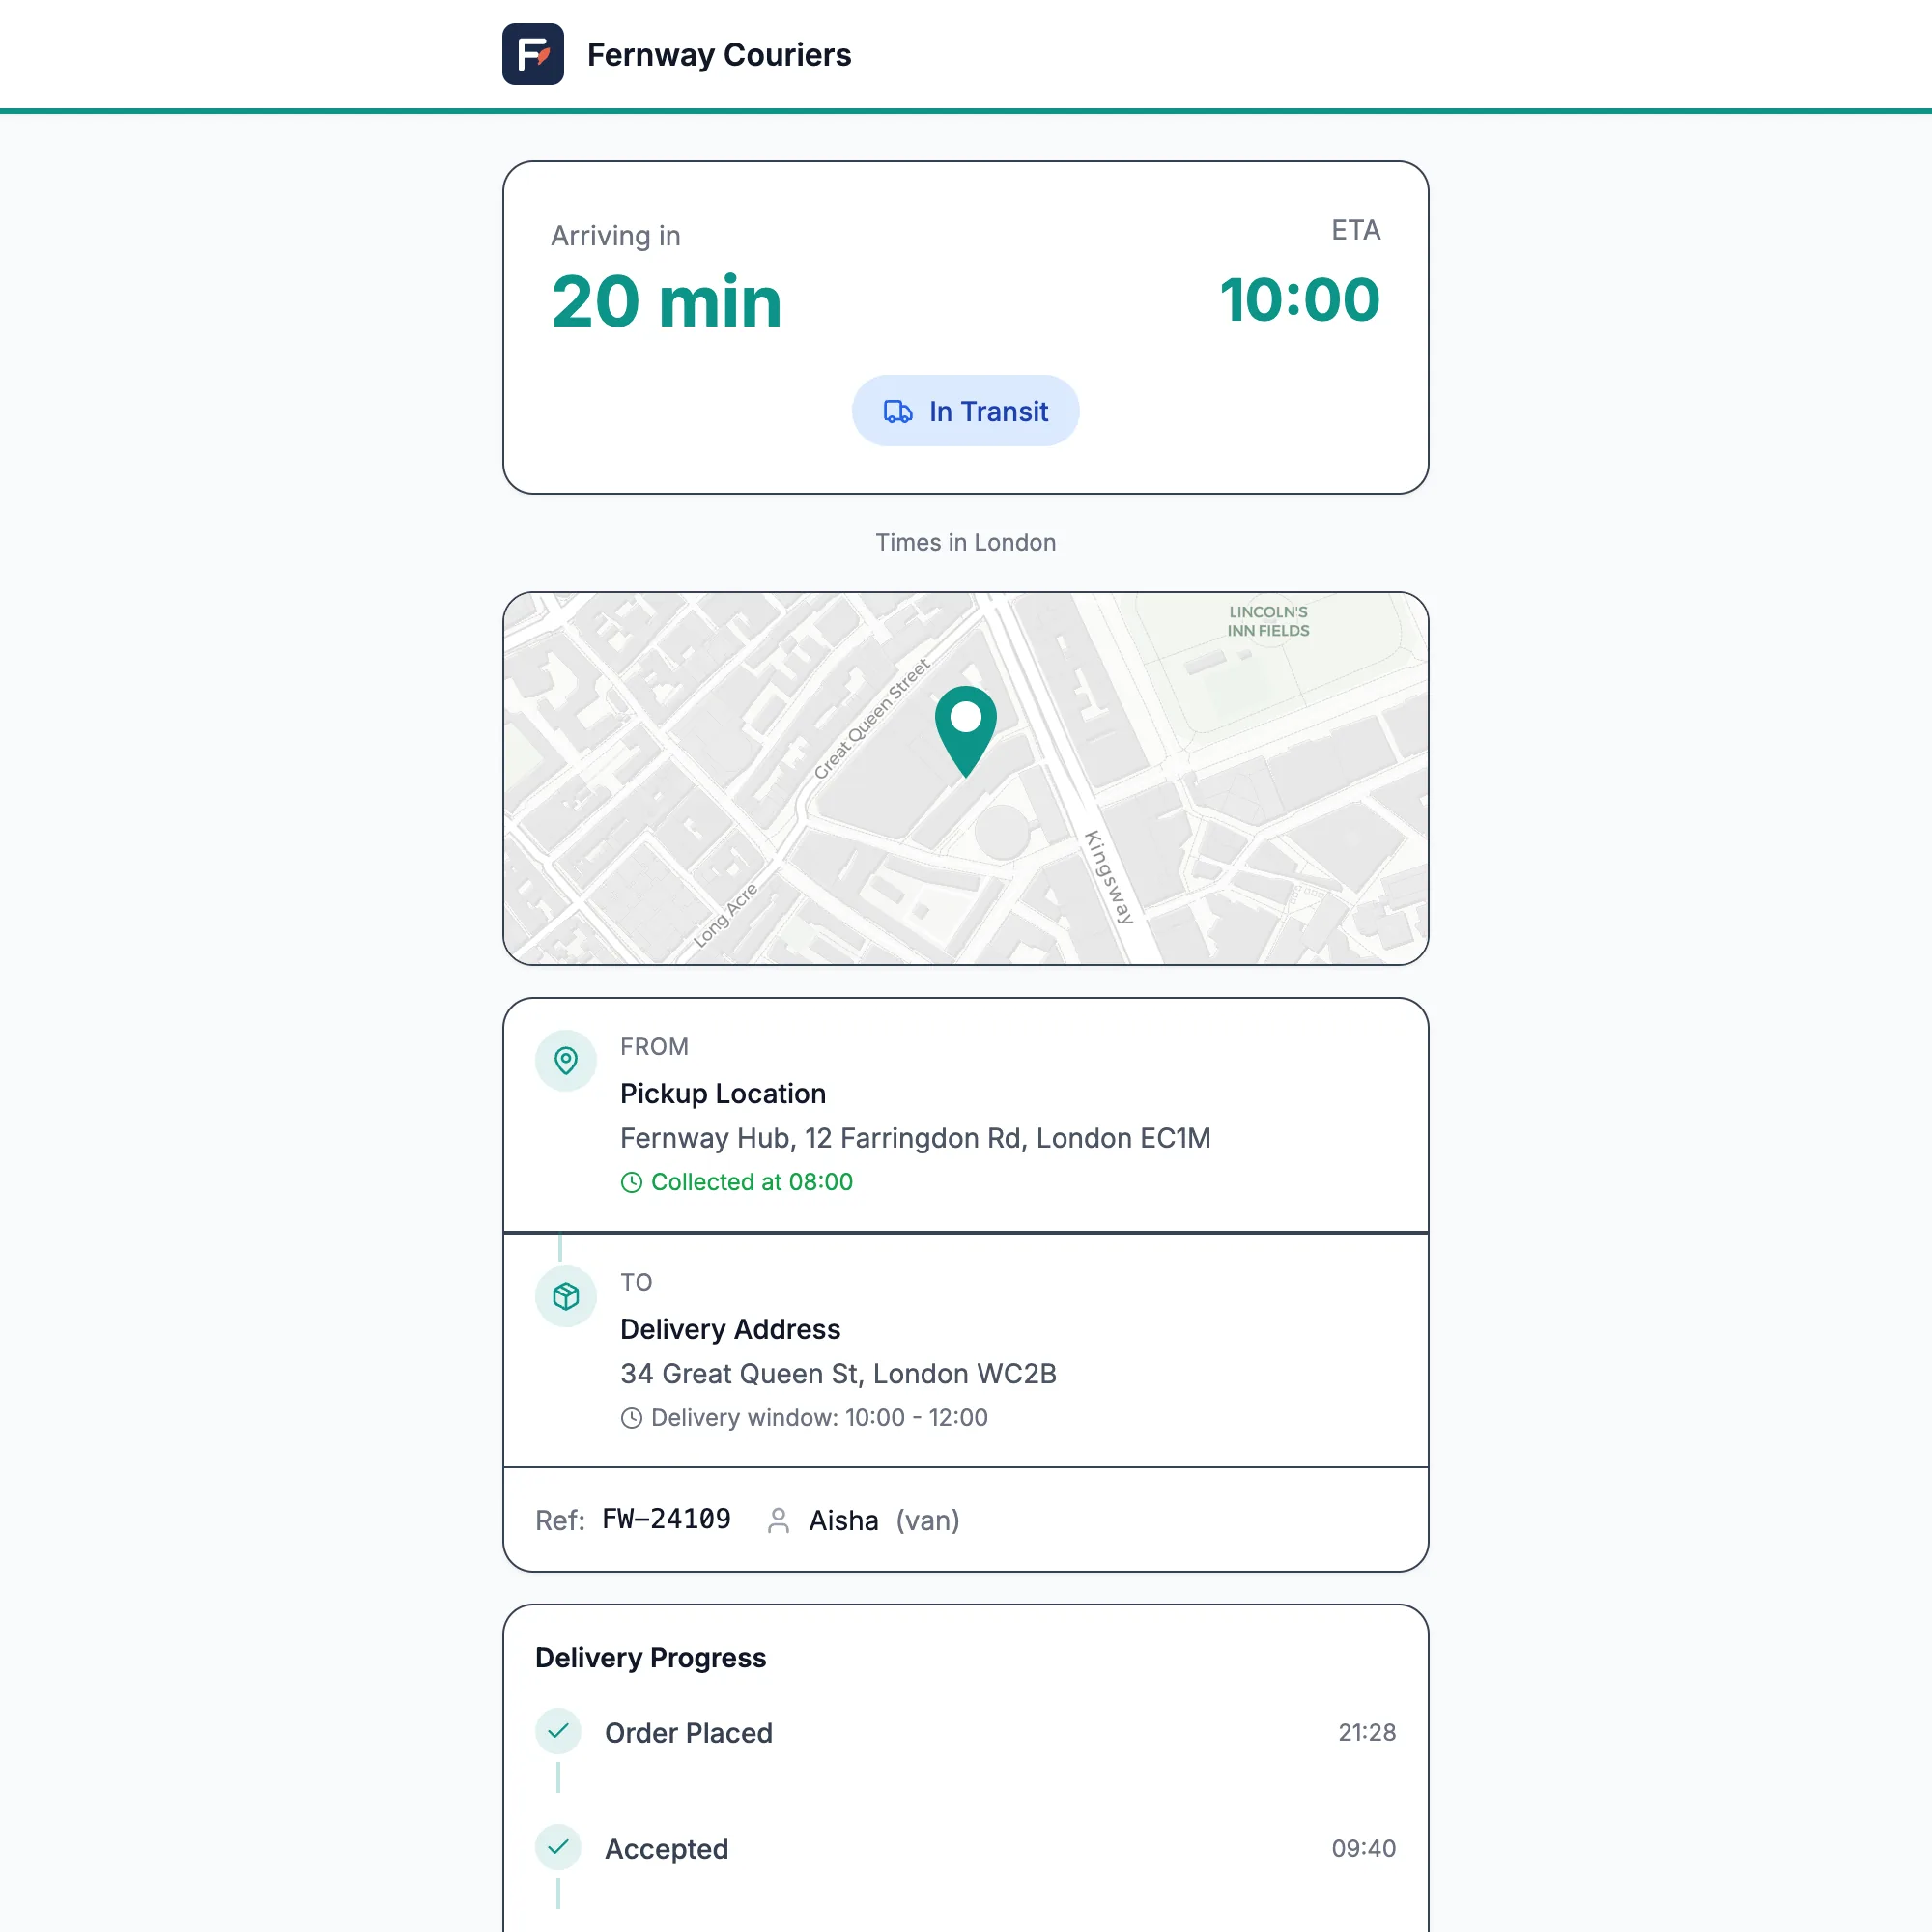
Tracking links are long and random. The customer confirms their postcode before the address, driver or exact ETA appear.
Repeated wrong tries lock the link for a while.
Audit trail
Who did what, and when.
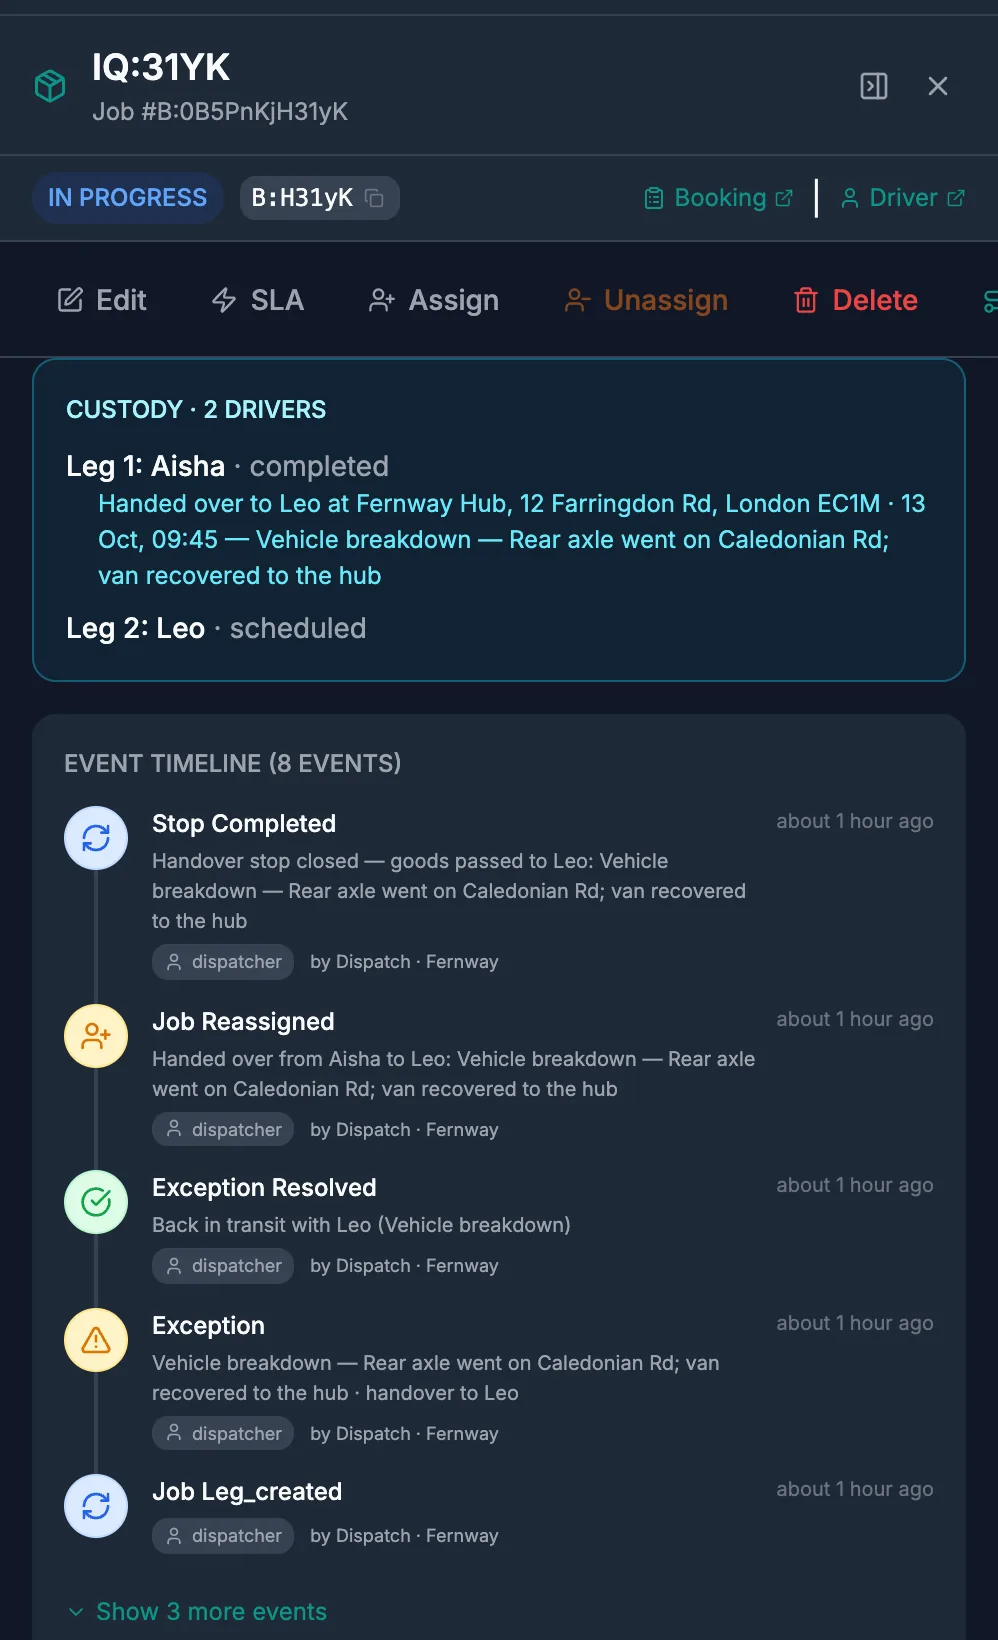
Bookings, jobs, stops and routes keep a record of who changed what, when and why.
Event log
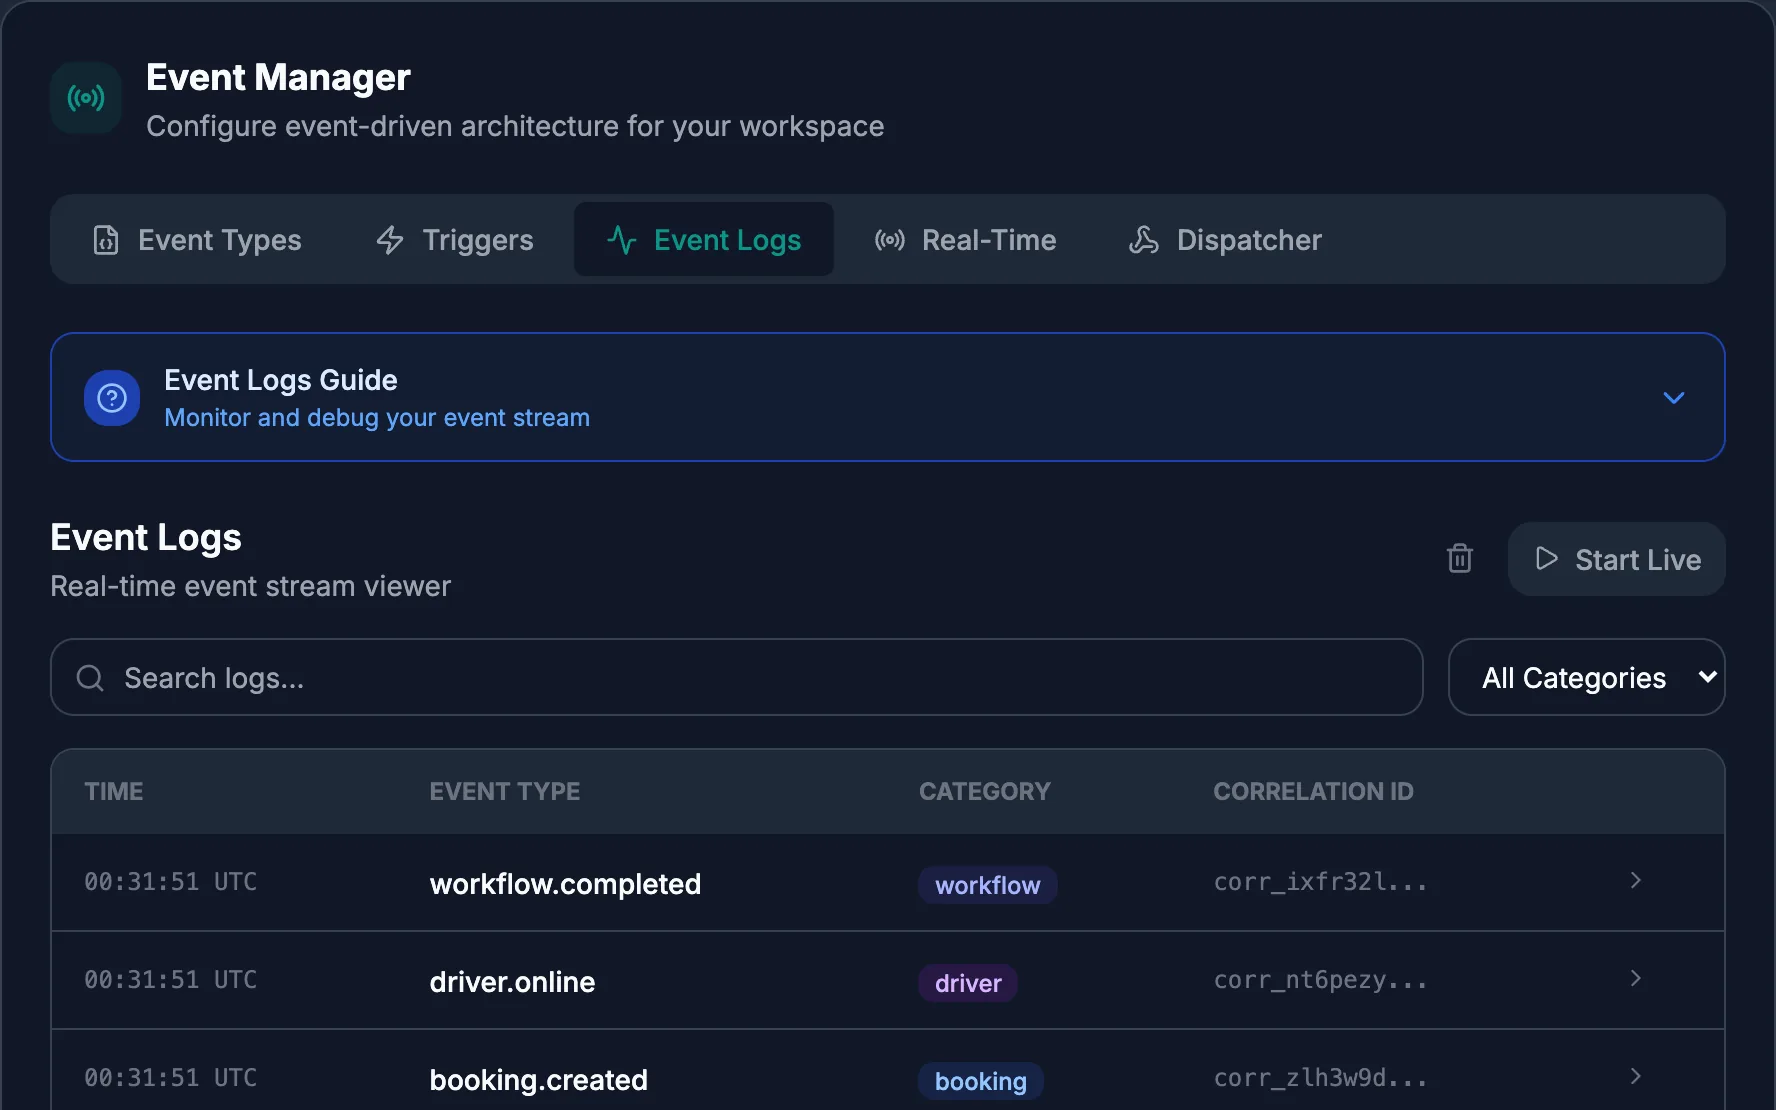
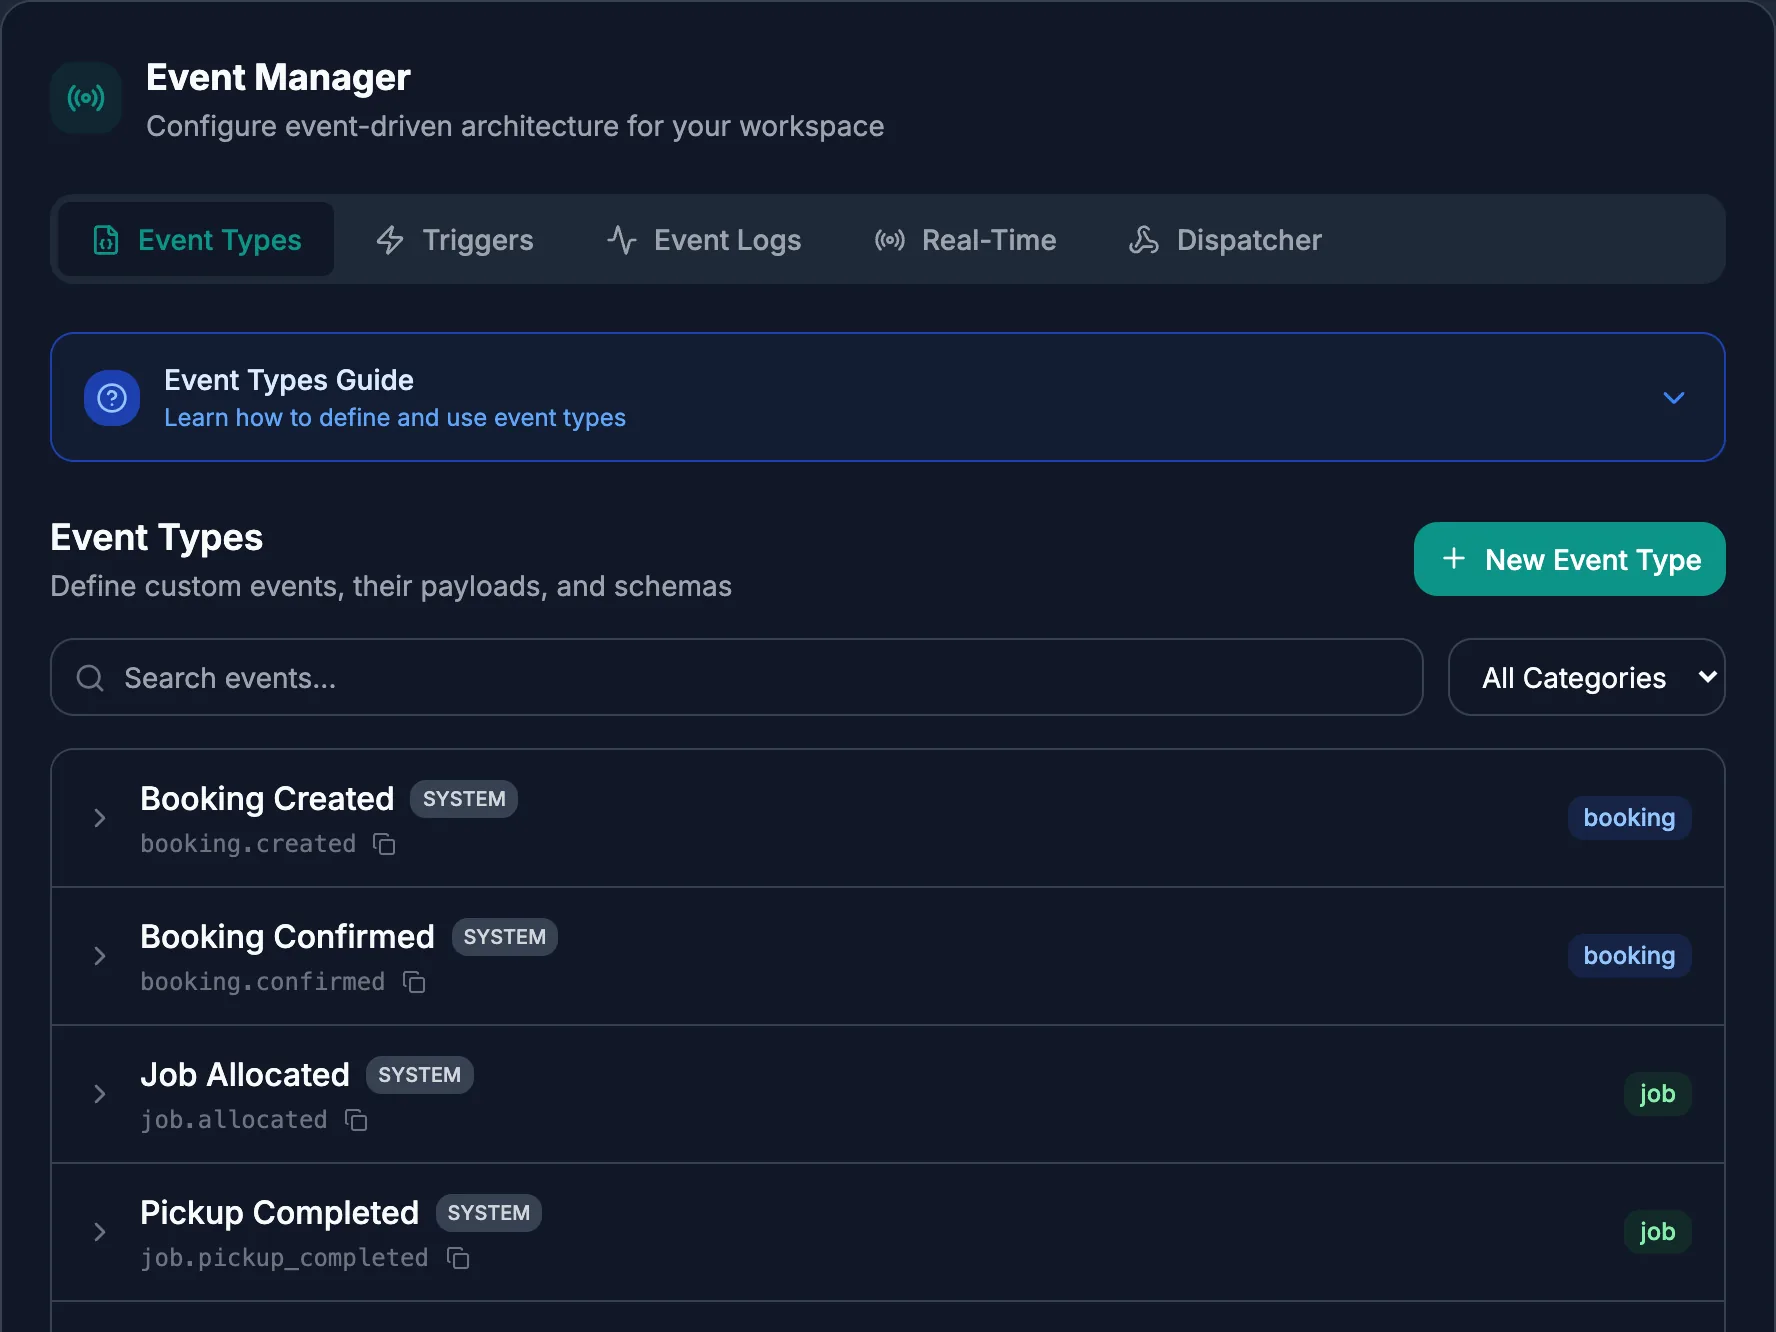
Every change is an event on the record.
Changes are written as events, so the history of a booking can be read back in order.
Webhooks
Signed, so you can check where they came from.
Outgoing webhooks are signed so your system can check where they came from, and are retried if they fail.
Retention
Kept as long as you choose.
Reporting a vulnerability
If you believe you have found a security vulnerability in OmnioIQ, tell us before disclosing it publicly. Email office@omnioiq.com with enough detail to reproduce the issue. We will acknowledge your report and keep you updated while we investigate.
Security review
Running a vendor assessment and need more than this page? Write to sales@omnioiq.com and we will work through your questions with you.